
• NIS2
  • DORA
  • MiCA
  • TPRM

Engineered cybersecurity
for regulated business
across EU jurisdictions

We don't sell paper reports — we build technical defense that stands up to both the regulator's audit and a real cyberattack, turning each country's requirements into your resilience.

  • Business stays online
  • Payments never frozen
  • Management stays protected
Our Services

Rules are
stricter.

Pressure is
mounting.

Greater
accountability.

  1. 1

    Cyber resilience has become a requirement,

    not just a recommendation, and the list of affected organizations is no longer limited to major industry players.
    EU regulators and business partners demand proof of your cyber resilience.
    The price of non-compliance is a lost contract, market exit, and severe fines.

  2. 2

    Cyber threats are no longer just an IT issue

    Today, they are the personal responsibility of executive management, extending directly to your suppliers. You are liable for security incidents originating from a vendor and for risks outside your direct control. Ignorance will no longer protect you from regulatory enforcement or personal liability.

  3. 3

    Regulators audit technical implementation, not paperwork.

    Partners demand real proof, not just a self-assessment questionnaire.
    When actual posture deviates from documentation, the consequences are tangible: financial penalties, loss of operational control, revoked licenses, or market exclusion.

A directive is
merely a framework.

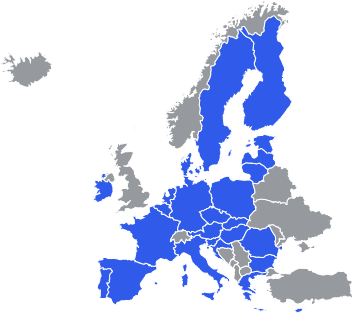
Reality lies in how each EU member state transposes it into national law. Local deadlines, national regulators, unique requirements — this is where generic compliance fails, and where most providers stop.

Map of EU member states

We go further:

jurisdiction-specific expertise combined with end-to-end support in dealing with regulators and insurance providers during incidents.

Where
do you need
confidence
first?

Bringing your infrastructure into full NIS2 compliance — assessment, gap remediation, verifiable evidence base, and operational framework optimization to guarantee successful regulatory audits.

For you if:

  1. You are designated as an Essential or Important Entity under NIS2
  2. You operate in a regulated sector or are expanding into the EU market
  3. Regulators or key partners require you to prove your cyber maturity

You get:

More than compliance — a competitive edge.

Executive protection against fines, trust from partners who see you as a resilient link, and streamlined security processes that keep your business online without slowing growth.

→ NIS2 Compliance detailed

Not sure about your true risk exposure?

Get clear answers with a quick evaluation

Book a call

The traditional

Industry approach is identical everywhere — force a one size fits all template

  • NIS2 ISO / NIST / CIS this results in a patchwork of standards stitched together to fit the directive.
  • TPRM vendor assessments, it means sending out identical, generic questionnaires to everyone.

The result is superficial compliance that fails under real-world scrutiny or cyberattacks.

For us

Industry standards are a foundation, not a pre-packaged answer

That is why we operate using our proprietary methodology.

Our methodology

RATE Regulatory Assessment through Traceable Evidence

Built on the core principle: From requirement to fully justified solution.

  1. 01 Requirement
  2. 02 Control
  3. 03 Evidence
  4. 04 Assessment
  5. 05 Gap
  6. 06 Risk
  7. 07 Scenario
  8. 08 Remediation
  9. 09 Verification

The starting point is always the specific regulatory requirement, which directly dictates the evidence, risk model, and tailored technical solution.

Our
approach

A documented control does not mean it effectively functions in practice.

We evaluate your actual security posture, not just stated policies, delivering true defensive capability instead of paperwork assumptions.
Every conclusion is fully traceable in both directions: top-down from executive decision to supporting technical evidence, and bottom-up from evidence to strategic action.

Zero reliance on assumptions: any decision can be audited back to its root source at any given moment.

We tailor our evaluation to your unique business environment: industry sector, geographic footprint, business model, and strategic objectives. The same regulatory requirement is addressed differently for different organizations based on their specific risk profile and operational priorities.

Tailored engineering solutions, not a generic checklist.

We do not walk away after handing you a list of deficiencies. We support you continuously until risk is genuinely mitigated. Going beyond remediation, we establish robust operational processes that prevent new vulnerabilities from arising.

You get a resilient, managed security posture — not a report sitting on a shelf.

Our methodology is integrated into a unified software system: centralized registry, evaluations, risk management, remediation workflows, and continuous monitoring.

Compliance transitions from a chaotic one-time initiative into an ongoing, manageable business process.

Assessment through evidence, not self-declaration

A documented control does not mean it effectively functions in practice.

We evaluate your actual security posture, not just stated policies, delivering true defensive capability instead of paperwork assumptions.
NIS2 DORA MiCA GDPR CSDDD PSD2 AMLD

+ Sector-specific MFSA / AIFMD / MGA and others

Regulatory Coverage

We cover the full spectrum of digital and financial EU regulations: NIS2, DORA, MiCA, GDPR, CSDDD, PSD2, AMLD, alongside specialized sector-specific standards (MFSA, AIFMD, MGA, and others). We also account for cross-border regulatory frameworks outside the EU wherever your business extends beyond the European perimeter.

We go deeper across every framework:

  • We factor in localized jurisdictional requirements alongside baseline ENISA guidelines
  • We evaluate multi-jurisdictional legal structures and third-party risks based on vendor origin
  • We provide active representation with regulators and insurance providers during active security incidents
  • We identify safe expansion pathways — guiding market entry and establishing processes tailored to local authorities

Threats strike from unexpected angles

whether from regulatory enforcement naming non-compliant entities publicly (NIS2/DORA, Art. 32) or a breach via a third-party vendor.

The impact is identical. Here are real-world cases:

  • TPRM

    Software Vendor

    2,600 Impacted Companies

    A single vendor vulnerability affected 2,600 organizations and 77 million individuals — most of whom had no direct contractual relationship with the vendor.

    Billions in damages · Risk inherited through third-party supply chain

  • TPRM

    Contractor with Excessive Access

    Operational Shutdown

    An attack compromised the internal network through a vendor with excessive system privileges. Non-critical to core business, but critical to security.

    Tens of millions in losses · Executive dismissals and complete operational shutdown

  • NIS2

    IT Outsourcer Hit by Ransomware

    €16M Fine

    An IT outsourcing provider supporting critical business processes suffered a ransomware attack. Regulators identified systemic failures: failure to contain privilege escalation, ignored alerts, and lack of security testing.

    €16M fine for gross negligence (not the breach itself) · 7M customers affected

  • MiCA / DORA

    Crypto Exchange

    Exit from Entire EU Market

    Failed to obtain a MiCA license prior to the deadline due to inadequate regulatory preparation — halting operations across the entire EU in 2026. EU oversight authorities permanently barred entry.

    Regulatory failure resulted in the loss of an entire continent market, not just a contract

Key Facts About Core Team

Denis Kiperidi

Denis Kiperidi

Head of Cybersecurity Strategy & Solutions

“Launching new ventures, scaling internationally, or adapting to regulations shouldn't feel like a minefield. Cybersecurity isn't a penalty tax—it's a strategic pillar. We are hands-on practitioners, not theorists or finger-pointers. There is no judgment here. Acting as explorers and pathfinders, we walk alongside your business to turn every new market, partnership, and product into lasting success and absolute confidence.”
  • Maksim Zhurbenko

    Maksim Zhurbenko

    Cybersecurity Governance & Regulatory Assurance

  • Hryhoriy Vashchuk

    Hryhoriy Vashchuk

    Information Security & GRC Advisory

    • MSc Information Security
    • BSc Computer Science
    • Information Security & Regulatory Compliance
    • Critical Infrastructure Protection
  • Maksym Kalchuk

    Maksym Kalchuk

    Offensive Security & Red Team Operations | Cyber Operations Leadership

You cannot manage a risk you cannot see.

Take the first step toward cybersecurity confidence and regulatory resilience for your organization and leadership.