NIS2

We build what regulators want to see and attackers want to avoid.

NIS2 compliance at the infrastructure level, not just paper policy — from assessment to an audit-ready evidentiary foundation.

Book a call

NIS2 (Directive 2022/2555) expands cybersecurity beyond traditional critical sectors — now covering Essential and Important entities, many of which still do not realize they fall within its scope.

However, the real story goes beyond the text of the directive.

The market has already shifted: organizations initiating NIS2 transformation now require proven cybersecurity maturity from their partners and vendors — filtering out those who delay. Regulatory enforcement is merely the first layer of pressure. The second, more impactful layer comes directly from your own clients.

What is happening right now

  1. regulators audit real security posture rather than paperwork:

    imposing fines up to 2% of annual turnover for gaps between written policies and actual controls.

  2. Market dynamics have changed:

    companies with verified maturity remove unprepared vendors from supply chains — leading to lost contracts before formal audits begin.

  3. Time is against you:

    waiting for full market adoption forces organizations into crisis mode — resulting in premium consultant rates, reactive troubleshooting, and operational disruption.

Our conclusion is straightforward: the question is no longer "if this affects us," but rather "will we prepare proactively, or react in crisis mode when issues arise."

NIS2

This is for you if:

  • You are classified as an Essential or Important entity under NIS2
  • You operate in a regulated sector or are expanding into the EU market
  • You form part of a European business supply chain (even if based outside the EU)
  • You are required to demonstrate cybersecurity maturity by regulators or corporate partners

This applies to you — even if it seems otherwise:

"We are not critical infrastructure"

— NIS2 extends far beyond traditional critical sectors, covering a significantly broader range of enterprises.

01/03

Check whether you fall under NIS2 and verify your category

Quick Assessment

Translating complex NIS2, DORA, and MiCA requirements into clear engineering tasks

The deliverable is a structured project with an audit-ready evidentiary baseline, not a simple list of findings.

  1. 1

    We align

    your organization with NIS2 requirements directly within your infrastructure, moving beyond simple document management.

  2. 2

    We define

    your scope and critical assets,

  3. 3

    Benchmark

    actual technical controls against directive mandates,

  4. 4

    Translate

    identified gaps into quantified business and regulatory risks,

  5. 5

    Build

    a prioritized remediation roadmap.

Comprehensive value

Through our engagement, you receive a functional compliance framework rather than just an assessment, including:

NIS2 Methodology

Proprietary
Methodology

Tailored to NIS2 specifications, featuring a five-step framework from initial evaluation to secure execution (RATE-based):

  1. 1

    Assessment

    defining scope and critical assets according to NIS2 criteria, ensuring resources focus on elements impacting business continuity.

  2. 2

    Gap Analysis

    evaluating operational controls against directive requirements beyond static policies to deliver a clear gap inventory.

  3. 3

    Risk Mapping

    translating operational gaps into business and regulatory risks, providing executive management with objective priority justifications.

  4. 4

    Remediation Action Plan

    establishing a prioritized roadmap with defined owners, timelines, and acceptance criteria, ensuring defensible audit outcomes.

  5. 5

    Implementation Support

    guiding execution by addressing priority gaps and preparing evidence for regulatory evaluation.

Evaluations follow a structured, end-to-end chain:

  1. Domain
  2. Requirement
  3. Control
  4. Evidence
  5. Gap
  6. Risk
  7. Remediation

This methodology ensures full traceability from empirical findings to strategic decisions — linking every risk back to supporting evidence and every action to a specific risk.

You receive a complete deliverable package — from initial diagnostics to execution control tools.

Diagnostics (Current State):

  • Compliance Matrix

    mapping NIS2 status per requirement (No Gap / Partial / Gap) linked directly to supporting evidence

  • Evidence Register

    a central artifact repository containing verified documentation suitable for regulatory submissions

  • Asset Register

    asset inventory categorized by criticality

  • Supply Chain Baseline

    vendor risk inventory categorized by access levels and operational impact

  • Incident Register

    tracking log connecting security incidents and near-misses to identified gaps and risks

Action (Remediation Execution):

  • Final Audit Report

    executive summary for the Board covering maturity metrics, critical risks, and estimated remediation costs

  • Remediation Plan

    actionable roadmap specifying item owners, timelines, and acceptance criteria

  • Management Dashboard

    tracking system to monitor task progress and vulnerability remediation

We cover NIS2, DORA, and MiCA — addressing cybersecurity for critical entities, digital operational resilience for financial institutions, and requirements for crypto-asset service providers.

We align directive requirements directly with your operational context — structuring our evaluation around your sector, jurisdiction, business model, and strategic goals.

While based on a unified EU directive, national transpositions create 27 distinct regulatory regimes:

holds executive directors personally liable even when duties are delegated

Customized solutions instead of standard checklists.

Generic templates overlook these nuances — we tailor implementation to your target operating country rather than relying on baseline ENISA documentation.

Engagement Models NIS2 Service Packages

All packages are delivered through our proprietary GRC platform, providing a structured and traceable digital environment for assessment, evidence management, risk evaluation, remediation and ongoing compliance activities.

Core

Assessment & Remediation

— A complete evidence-based NIS2 assessment designed to establish the organization’s current compliance position, identify control weaknesses and associated risks, and define the actions required to address them.

Outcome:

A clear, evidence-based view of the organization’s NIS2 readiness, identified risks and prioritized actions required to close compliance gaps.

Includes:

  • NIS2 applicability and requirements assessment
  • Control design and effectiveness evaluation
  • Evidence review and validation
  • Gap identification and analysis
  • Risk assessment and contextualized risk scenarios
  • Prioritized remediation recommendations
  • Core documentation package, including essential policy, procedure and standard templates
  • Digital assessment workspace within our GRC platform
Case Study Summaries

  • Case 1

    • Germany
    • Energy
    • 2,500 employees
    Before:

    ISO 27001 existed on paper only. Identity and Access Management (IAM) rights were overly broad, and supply chain oversight relied on unverified vendor questionnaires.

    What we did

    Completed end-to-end critical asset mapping, implemented Role-Based Access Control (RBAC), and conducted technical vendor audits — replacing unverified questionnaires with validated evidence.

    Result:

    Successfully passed federal BSI audit. Unauthorized access risk to power grid infrastructure was reduced from High to Low.

  • Case 2

    • Belgium
    • Logistics
    • 800 employees
    Before:

    Lacked centralized incident response procedures. The incident log recorded zero entries, though audit procedures uncovered unrecorded near-misses managed informally at the IT level.

    What we did

    Established continuous monitoring protocols, categorized historical incidents using a structured risk model, and trained Board members regarding personal liability exposure.

    Result:

    Secured regulatory approval from Belgian authorities, retaining key eligibility for public sector enterprise contracts.

  • Case 3

    • Poland
    • IT
    • 50 employees
    Before:

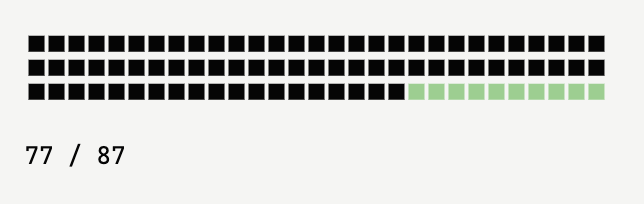
    77 out of 87 control areas non-compliant. Infrastructure blind spots, missing asset ownership models, severe IAM vulnerabilities, and no formal incident management framework, resulting in potential fines up to €10M or 2% of turnover.

    What we did

    Instituted a RACI governance matrix, integrated the Asset Register with Jira, applied a 1–5 asset criticality scale, and formalized vulnerability management workflows.

    Result:

    Assigned explicit ownership and criticality rankings across all assets, reducing unmanaged asset risk from Critical to Low while establishing foundational readiness for SOC/SIEM integration to support EU market expansion.

Key advantages of partnering with us:

01 Business Language

actionable execution plans mapped directly to business operations: ensuring full clarity on actions, objectives, and targeted risk mitigation

02 Engineering Practice, Not Just Advisory or Software

we operate as an embedded regulatory engineering unit. Rather than merely presenting issue reports, we resolve vulnerabilities directly.

03 Proprietary NIS2 Framework

purpose-built architecture complete with pre-drafted policy templates, avoiding conflicting, generic compliance standards.

04 Outcome-Based Pricing

defined scope, milestones, and deliverables agreed upon upfront, preventing budget overruns or hidden hourly billing.

FAQ

How long does the engagement take?

Timeline depends on project scope, including domain count, infrastructure scale, and current documentation maturity. Definitive timelines are established during scoping prior to kick-off, ensuring clear delivery expectations from the start.

Is system access required?

We require access to key stakeholders (IT, Legal, C-level) along with architectural and policy documentation. Technical evaluations remain at the architecture level, eliminating the need for direct access to sensitive production systems.

We hold ISO 27001 — is this sufficient?

No. ISO 27001 serves as a management framework and does not ensure regulatory compliance on its own. NIS2 mandates specific technical operational outcomes backed by legal and financial accountability.

How is confidentiality managed?

All engagement information is protected under NDA, and all resulting evidence remains your exclusive property.

Does this prepare us for official audits?

Yes. Evidentiary records are structured to withstand rigorous technical audits by regulatory bodies, extending beyond superficial documentation reviews.

We do not deliver a checklist. We deliver a traceable path from evidence to management decisions.

Contact us to identify your operational gaps and receive a detailed remediation estimate.